Krawl
A deception server that detects, delays and profiles attackers, web crawlers and automated scanners.
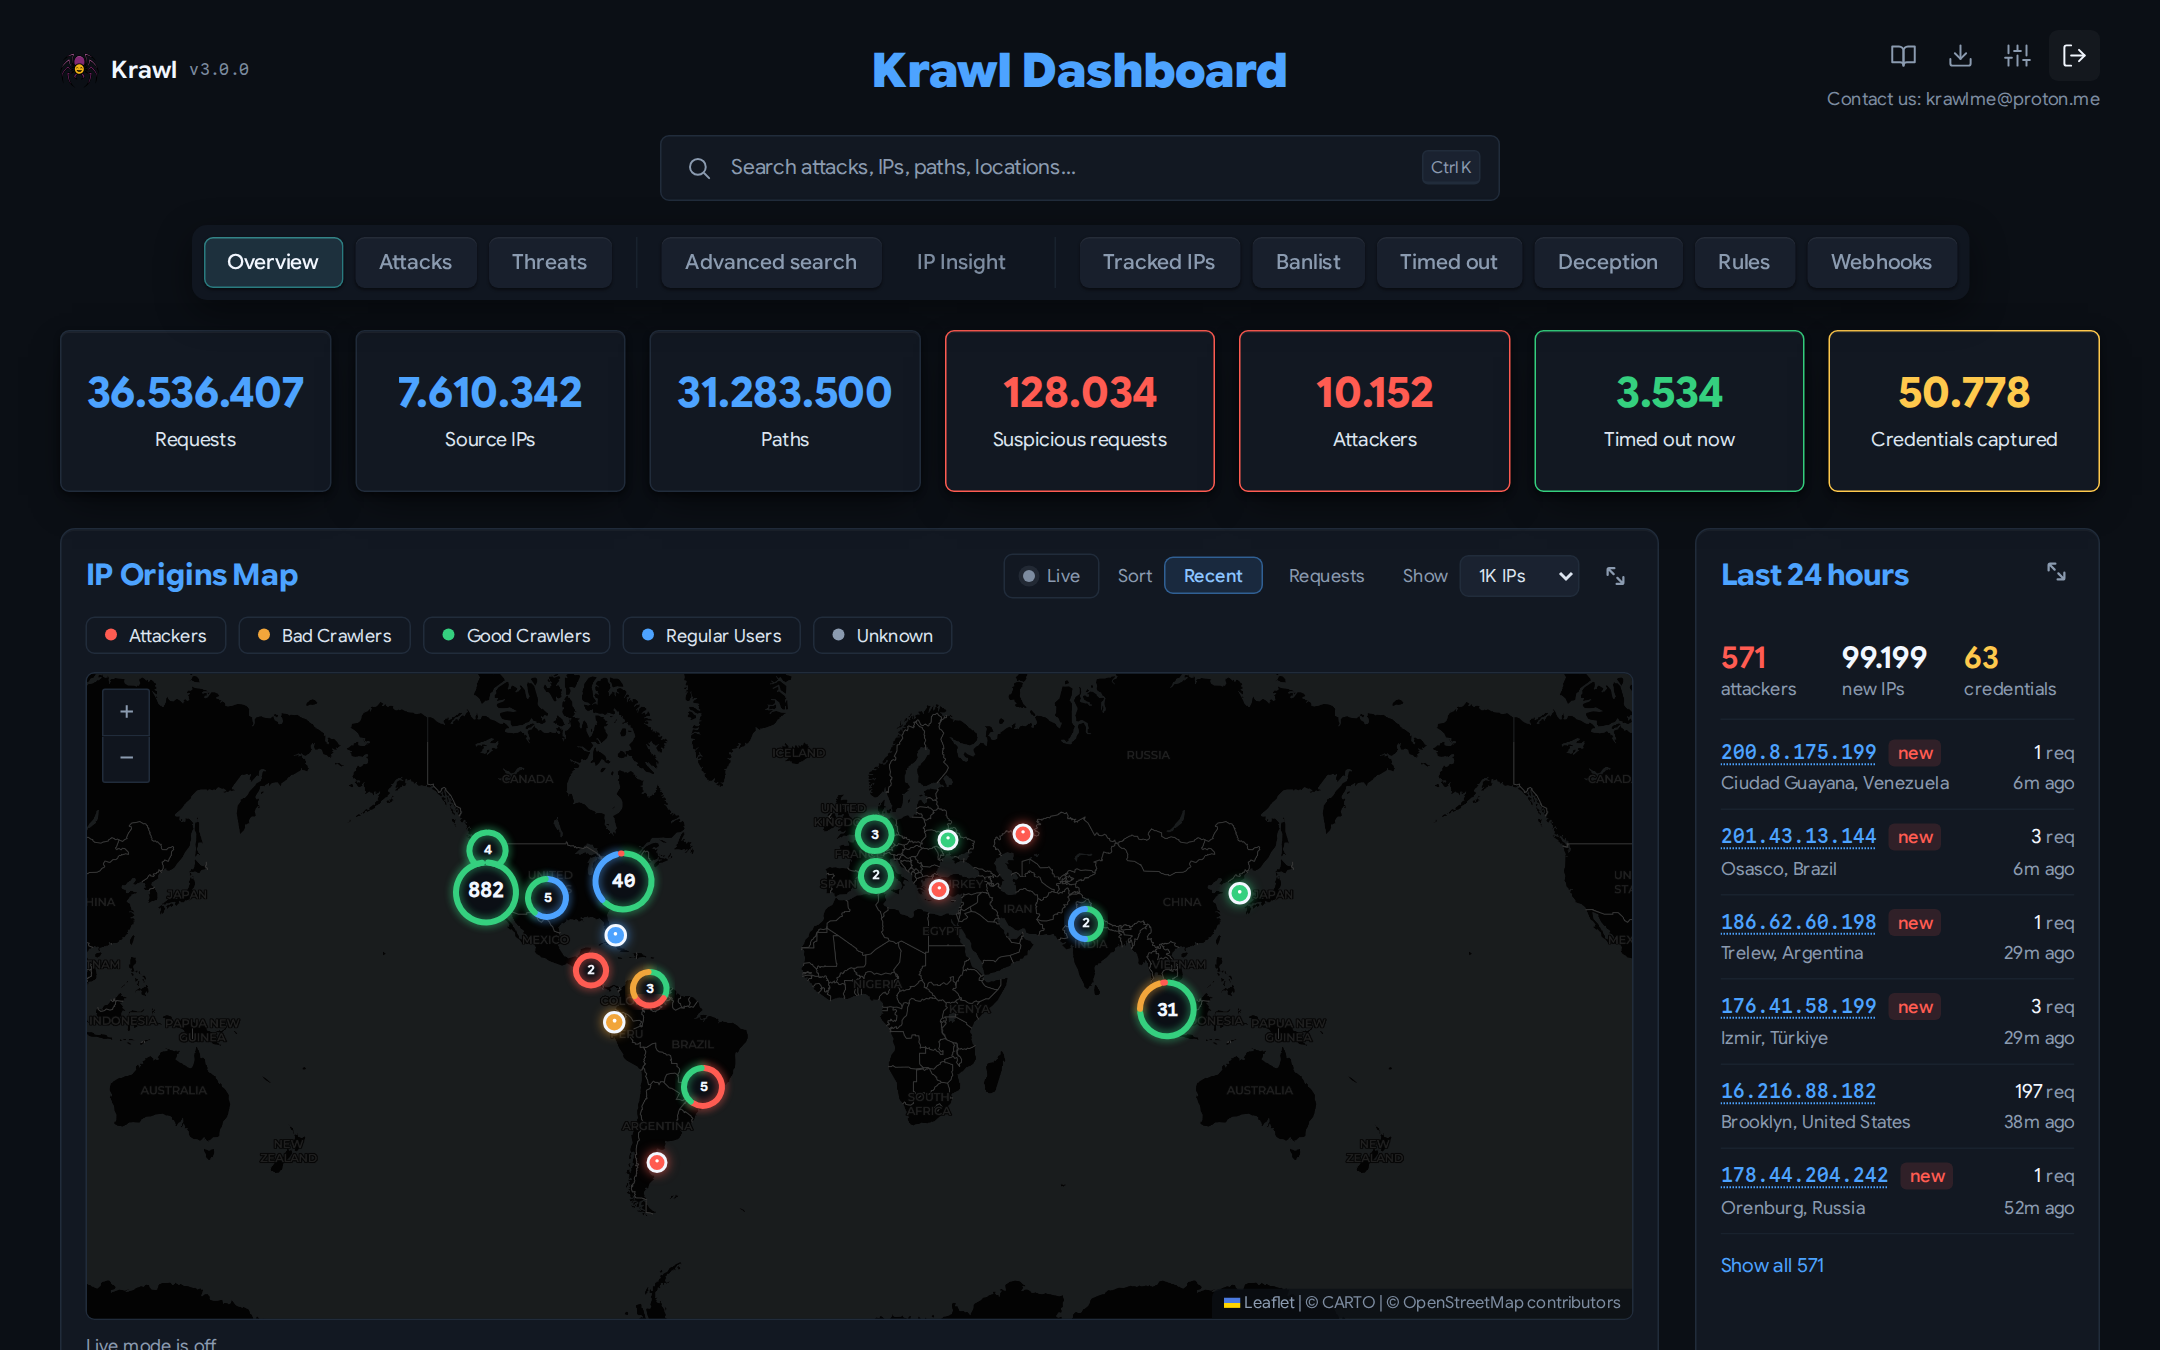
Krawl serves realistic fake applications, such as admin panels, exposed configuration files and leaked credentials. It detects attacks with YARA rules, answers each one with a convincing fake reply, and classifies every client IP by its behaviour. A dashboard shows all of it, and banlists export to your firewall.
Quick start
docker run -d \
  -p 5000:5000 \
  -e KRAWL_DASHBOARD_SECRET_PATH="/my-secret-dashboard" \
  -e KRAWL_DASHBOARD_PASSWORD="my-secret-password" \
  -v krawl-data:/app/data \
  --name krawl \
  ghcr.io/blessedrebus/krawl:latest
The trap answers on http://localhost:5000, the dashboard on
http://localhost:5000/my-secret-dashboard. Docker Compose, Kubernetes and
Helm are covered in Deployment modes.
Upgrading from 2.4?
Read Upgrading from 2.4 to 3.0 first.
Documentation
-
Set up
Configuration:
config.yamland everyKRAWL_*variable
Deployment modes: SQLite, or PostgreSQL and Redis
Reverse proxy: NGINX, CDNs and decoy subdomains
Upgrading from 2.4 to 3.0 -
How it works
Honeypot: bait pages and the
pages:manifest
Attack detection: YARA rules and fake replies
How IPs are evaluated: categories and pruning
Tarpit · AI generation · Deception pages · Canary token -
Use the data
Dashboard: every tab, with screenshots
Dashboard API: JSON API, with an API reference
Firewall exporters: raw, iptables, nftables
Cloudflare banlist · Monitoring -
Operate
Retention: how long each kind of data is kept
Backups: the scheduled database dump
External APIs: third-party IP data services -
Develop
Architecture: code layout, pipeline, schema, tasks
Coding guidelines: conventions for contributors